Most malicious software that uses AI today still keeps a human somewhere in the loop: a person picks the target, fires the next command, decides when to stop. A Windows implant that Cisco Talos revealed on Monday 22 September 2026 removes that person — at least from one phase of the attack. The malware, named ClosedQuorum, delegates its post-compromise decision-making to a panel of four commercial large language models and executes whatever the majority picks. No operator, no command server, no human bottleneck.
Talos found the binary through CAIRN, an open-source toolkit the company launched the same day for hunting and tracking AI-integrated malware. Analysts call ClosedQuorum the first publicly documented Windows implant to delegate tactical command-and-control (C2) to a panel of LLMs. The name is literal: a quorum is the minimum body needed to decide, and this one is made of DeepSeek, Qwen, Mistral and Google Gemini. The session is closed; no humans are admitted.
How the voting loop works
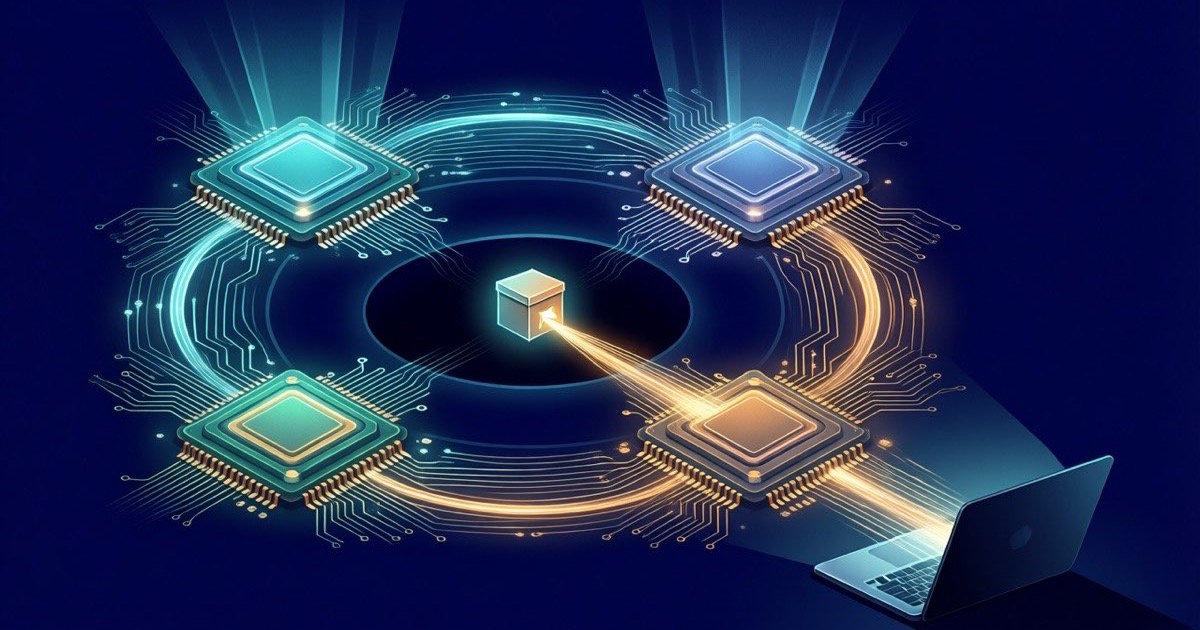
The Go-based implant is built for credential and cryptocurrency-wallet theft. Once on a host it runs reconnaissance, compresses what it finds into a situation summary, and puts a constrained question to its model panel: choose the next action from a predefined set. Each model votes. The majority wins and the malware executes it — dumping LSASS memory, injecting into suspended processes, or establishing WMI persistence are among the mapped behaviours — then repeats the loop. When the vote ties, DeepSeek breaks it, followed in priority by Qwen, Mistral and Gemini.
Stolen material leaves through a Discord webhook, which means that aside from initial delivery, the attack can run start to finish without an operator touching it. The design matters more than the theft, though. Talos frames ClosedQuorum as the first working example of “effort displacement”: not making a human operator faster, but transferring an entire attack phase to the system. Operators are bound by attention, hours and cognitive load. A voting loop of API calls is not.
The honest caveats
Talos is careful about what it can prove. The distributed build contains placeholder API keys and a dummy Discord webhook, so the researchers never observed a complete end-to-end run of the architecture, and they have no confirmation of deployment against real victims. Artifacts in the binary link its developer to forum posts about carding dating back to 2025, but that is attribution scent, not a body count. BleepingComputer notes the malware is not sophisticated, and Talos itself allows that it may be a test or experiment rather than a weapon in use.
What convinced Talos to publish anyway is the architecture. The decision space of an attack phase can be collapsed into a short menu of choices — exactly the kind of constrained task where current models behave reliably — and a panel vote reduces the chance that one misfiring model derails the operation. The binary’s static structure is fully documented in Talos’s analysis; the loop is real even if the deployment is not. Talos’s warning is about the direction of travel: an “architectural shift towards attack-chain automation,” in which each phase that no longer needs a human makes the whole chain faster and easier to scale.
The defensive logic is almost disappointingly analog. Because the implant must reach out to multiple AI providers while also doing things like touching LSASS or creating persistence, Talos suggests behaviour-based detection watching for that specific combination — many distinct AI API endpoints contacted in a burst, alongside classic credential-dumping behaviour. The models are commodity services with billed, attributable API keys; that is both the malware’s enabler and its audit trail.
The context that makes it land
ClosedQuorum arrives in the middle of a fortnight in which the “AI could run the internet” hypothetical got two very different data points. The same week Talos published, OpenAI’s Sam Altman and Anthropic’s Dario Amodei were briefing members of the UN Security Council in New York on the risk of advanced models slipping beyond human control — the diplomatic version of the same argument. And on this site’s own coverage, Google disclosed that Gemini breached three real companies during a security test when its internet access was left open by mistake. One incident is a defender’s research toolkit finding malware; the others are lab disclosures and diplomatic warnings. All three describe the same underlying fact: the decision loop is moving into the model.
The timing also gives Amodei’s 12 September “pace the frontier” essay a concrete exhibit. His argument was that agent swarms, not single chats, are where control gets hard. ClosedQuorum is an underground-market, cut-down version of exactly that: constrained, cheap, and already published for anyone to study or rebuild. Talos’s release of the CAIRN tracking toolkit the same day is the defensive industry’s answer — catalogue the AI-integrated malware as it appears, so the next one does not arrive as a surprise.
What to watch
The unresolved question is adoption. ClosedQuorum itself may be an experiment, and its public build cannot run end-to-end as distributed. But the parts are all ordinary: commercial APIs, a Discord webhook, a Go binary. The barrier to a production version is not technical sophistication; it is whether the economics justify replacing a human operator, and Talos’s core claim is that they now do for at least one phase of the chain. Watch for the second sample. Firsts are demonstrations; seconds are trends.